Understanding the Dashboard
The Dashboard is the WAS homepage when you are logged in. It gives you an overall idea of your environment’s security posture.
Site header
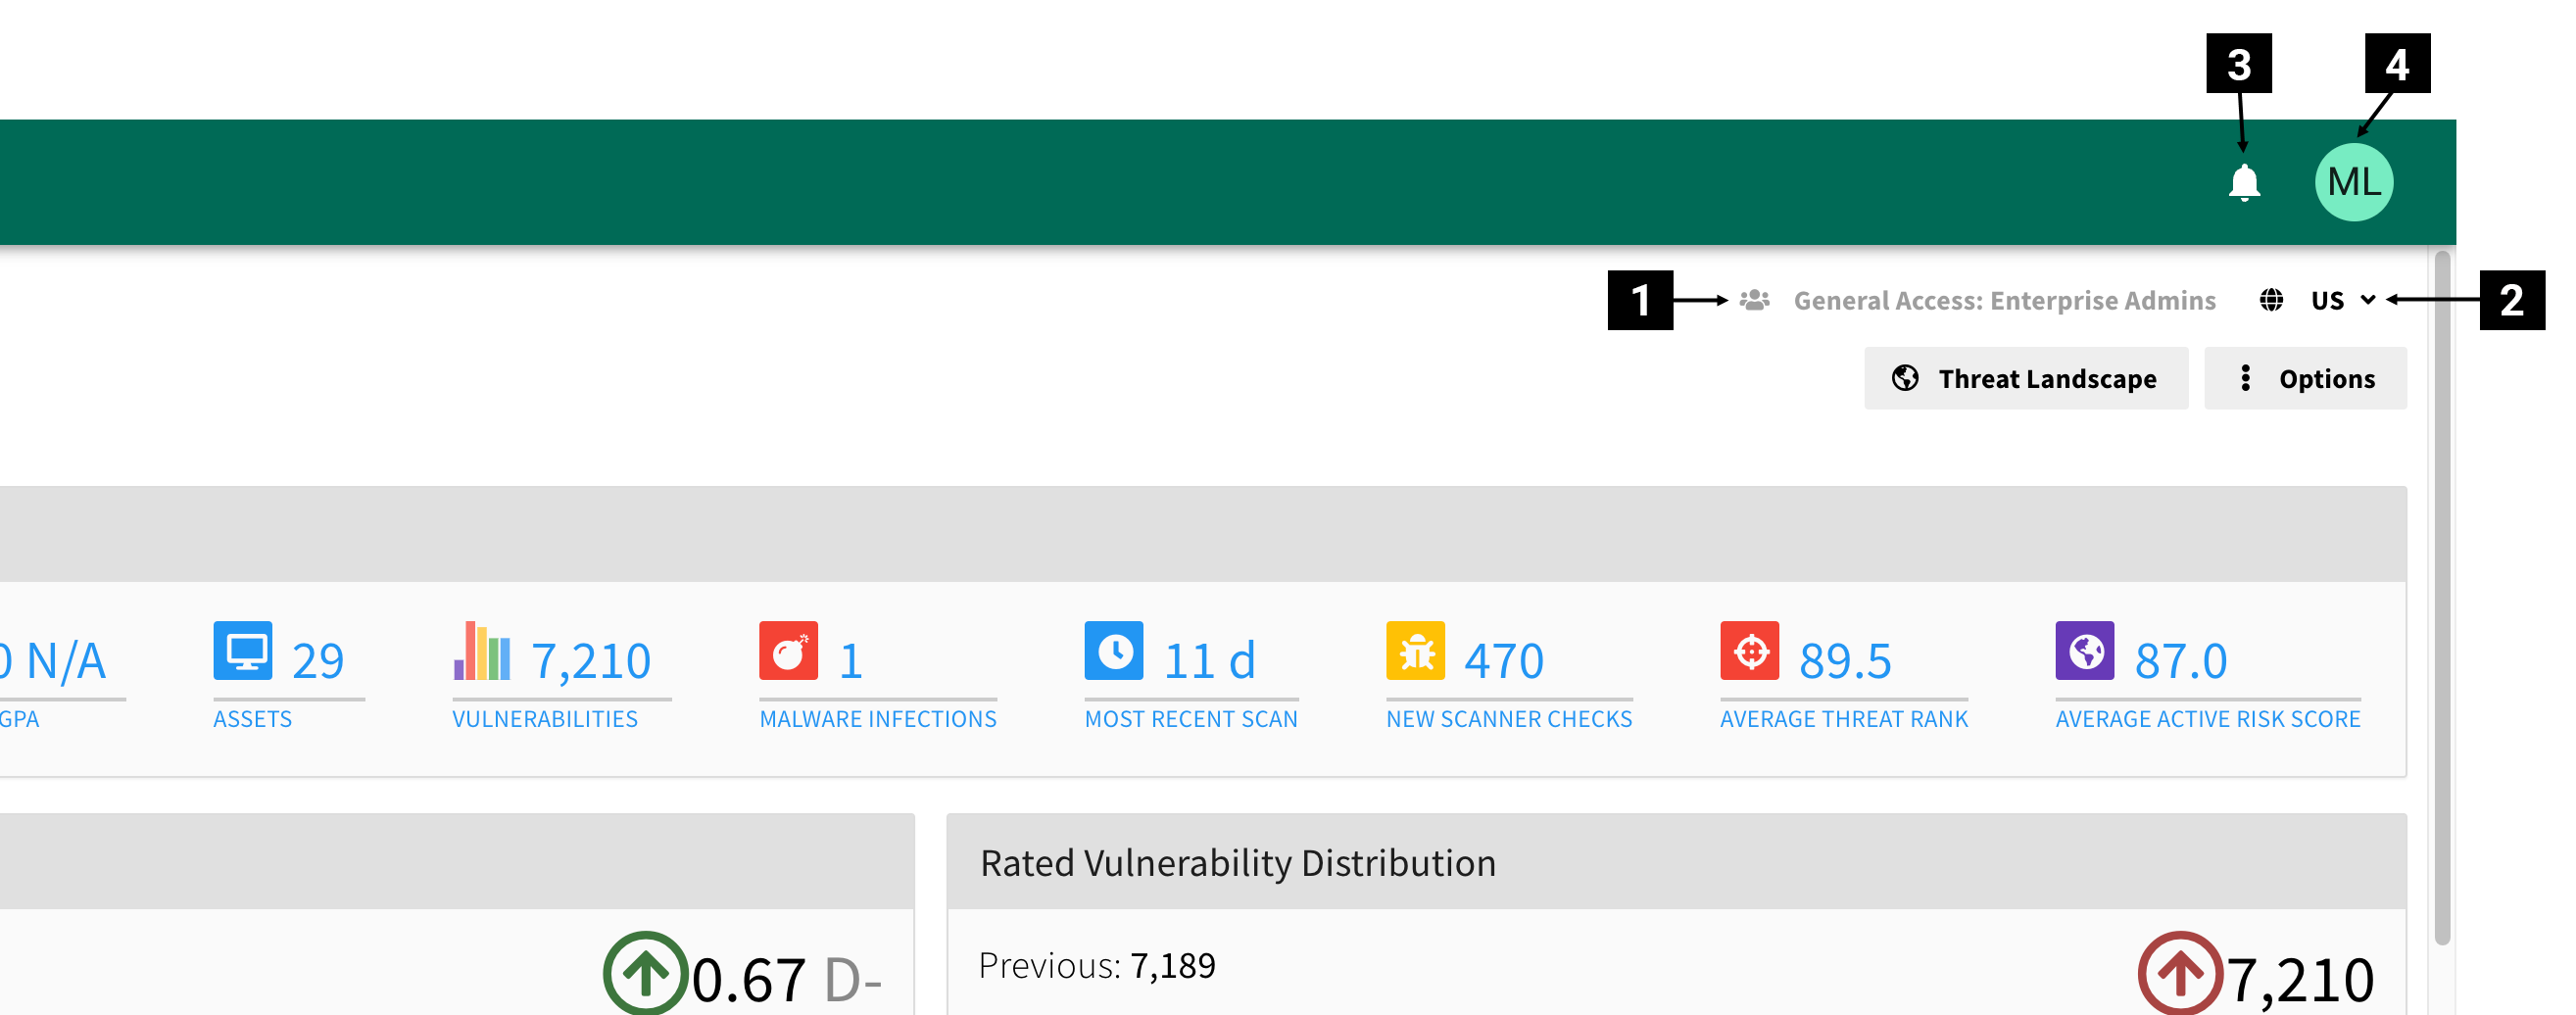
The site header, located on every page, grants access to some primary WAS features.
-
Business Group
All data and accessibility within WAS is filtered according to the selected business group's parameters. Define custom business groups according to your organization's needs and switch between each here in the header. To setup business groups, see Business Groups.
-
Region
The header will display the engaged region for your WAS product.
-
Notifications
Select the bell symbol in the header to see a display of notifications you received. The number of unread notifications will display with the envelope by a red number. To modify notification preferences, including email notifications, see Notifications.
-
User Menu
When selected, the user menu in the header will open a menu for access to My profile, Manage Notifications, Change Password, Hide help, Report an issue, and Sign out.
Navigation menu
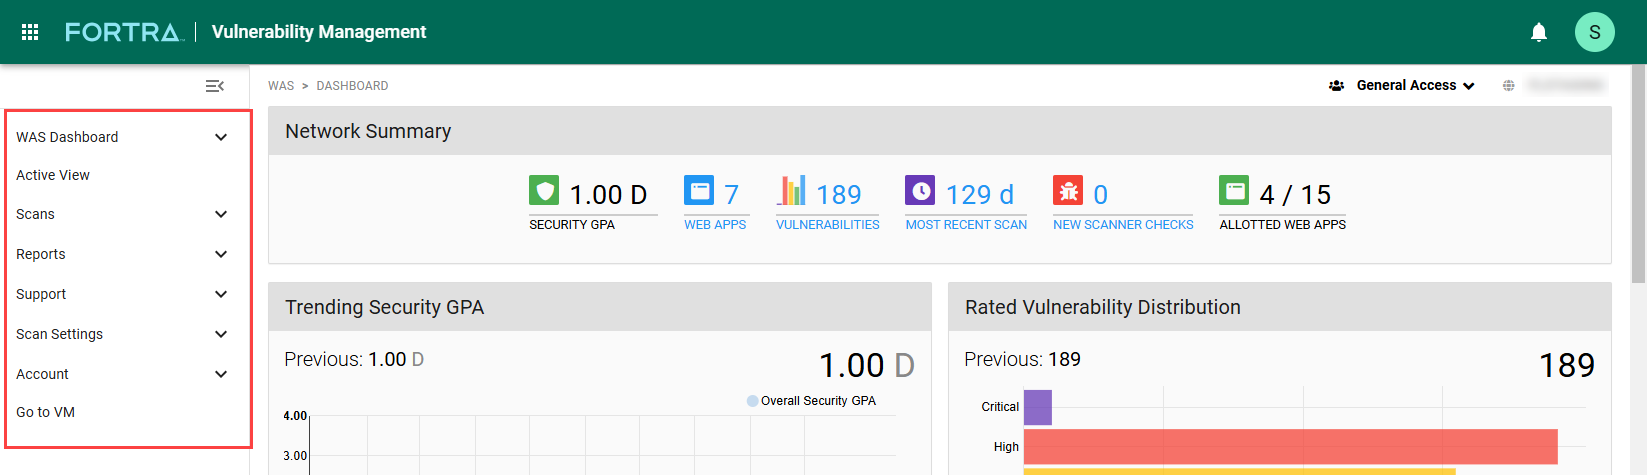
The navigation menu, located on every page, gives you access to WAS tools and features. Each item in the navigation menu will expand when selected to show additional options. The side navigation menu is your primary access point for all features within WAS.
Network summary
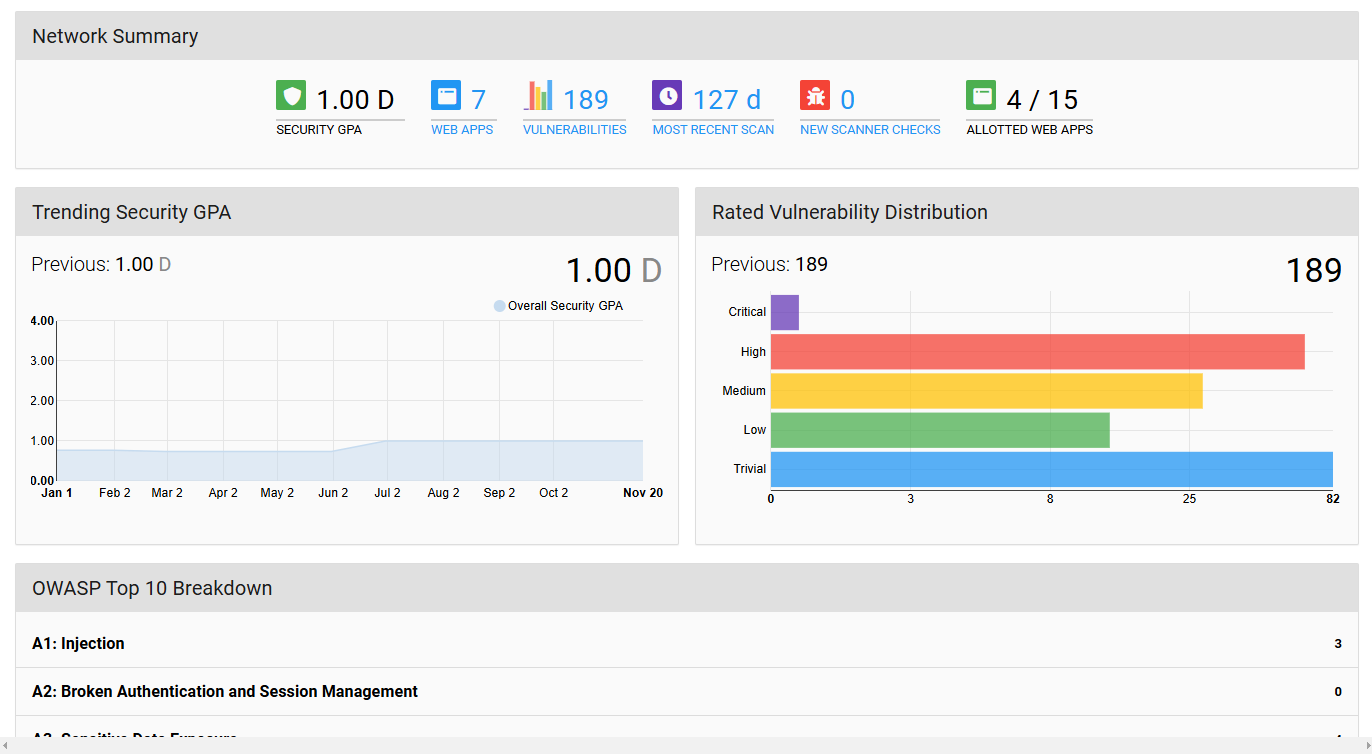
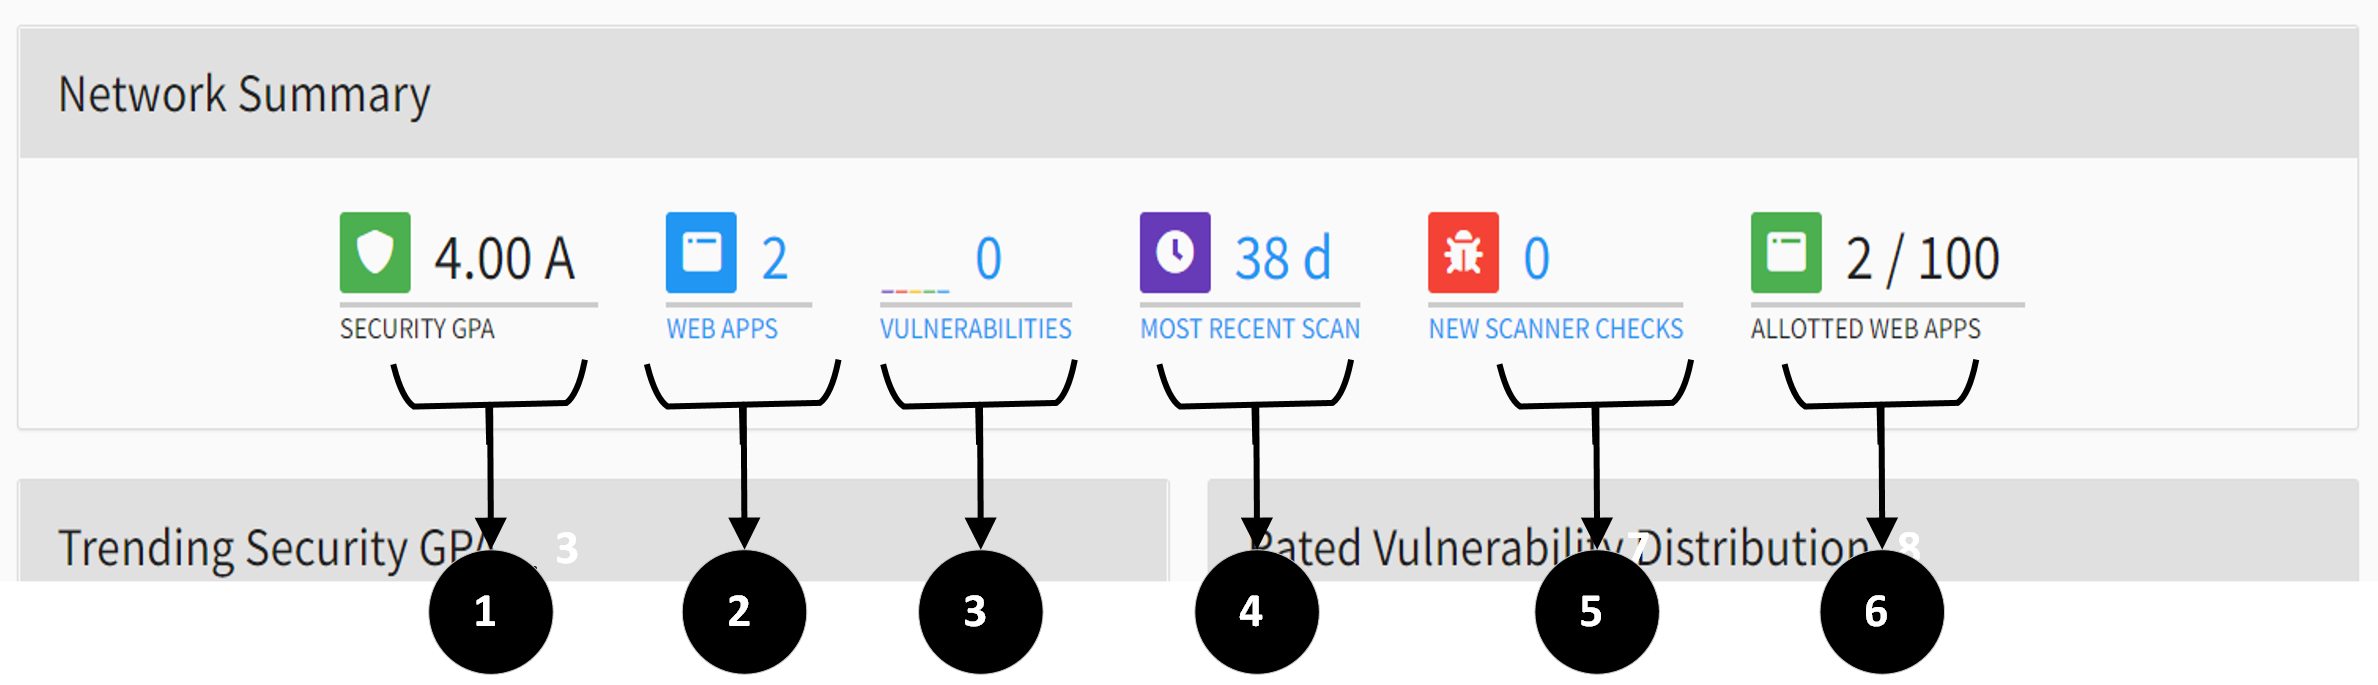
The Dashboard's Network Summary panel provides an overview of the network’s security posture. You can select each item for direct routing to filtered data used to quantify the displayed scores.
 WAS Network Summary components
-
Security GPA
The weighted average of evaluated web applications vulnerable to attacks.
-
Web Apps
The number of evaluated web apps.
-
Vulnerabilities
The number of vulnerabilities discovered in your environment.
-
Most Recent Scan
Time since the completion of a previous scan.
-
New Scanner Checks
The number of consolidated vulnerability checks (CVCs) newly added to the scanner.
-
Allotted Web Apps
The number of web applications currently utilized and allotted on your subscription
The At a Glance dashboard includes graphs that show vulnerability age and remediation-time trends. By default, only selected trend lines appear to highlight specific trends. Cloud statistics are also included in these graphs.
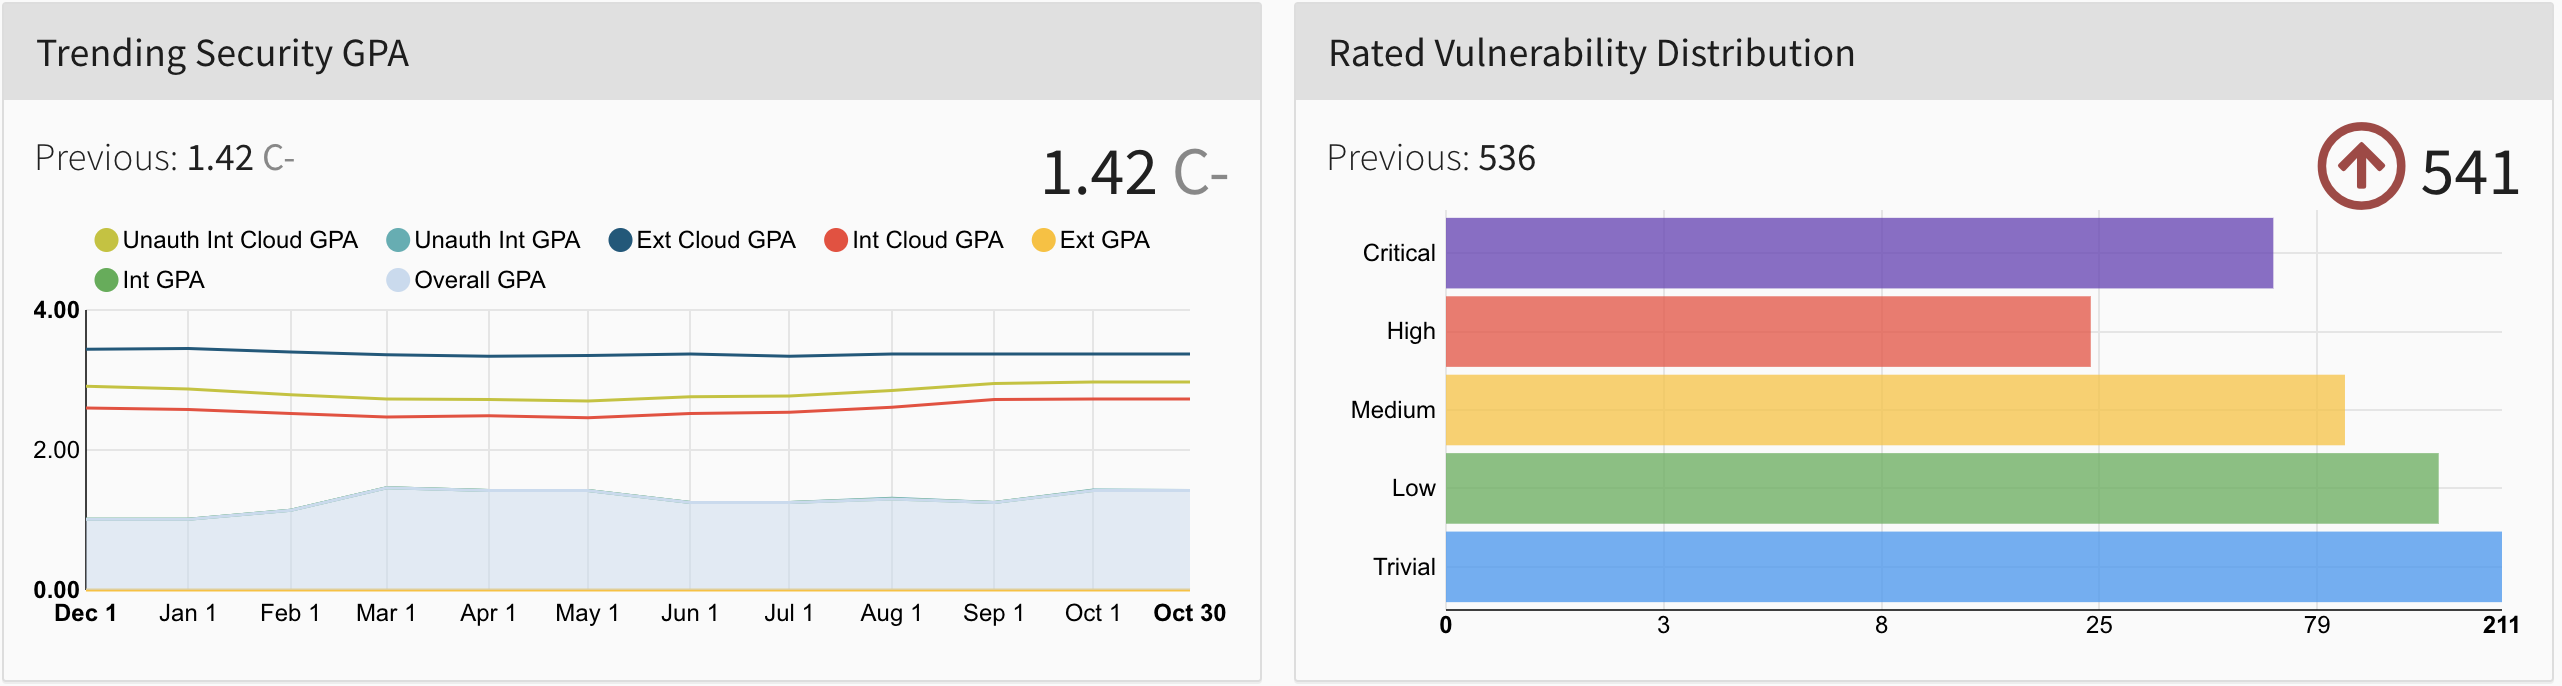
Security GPA trend graphs distinguish between Security GPA calculated from unauthenticated vulnerabilities and Security GPA calculated from all vulnerabilities. This distinction also appears in PDF reports.
Trending Security GPA
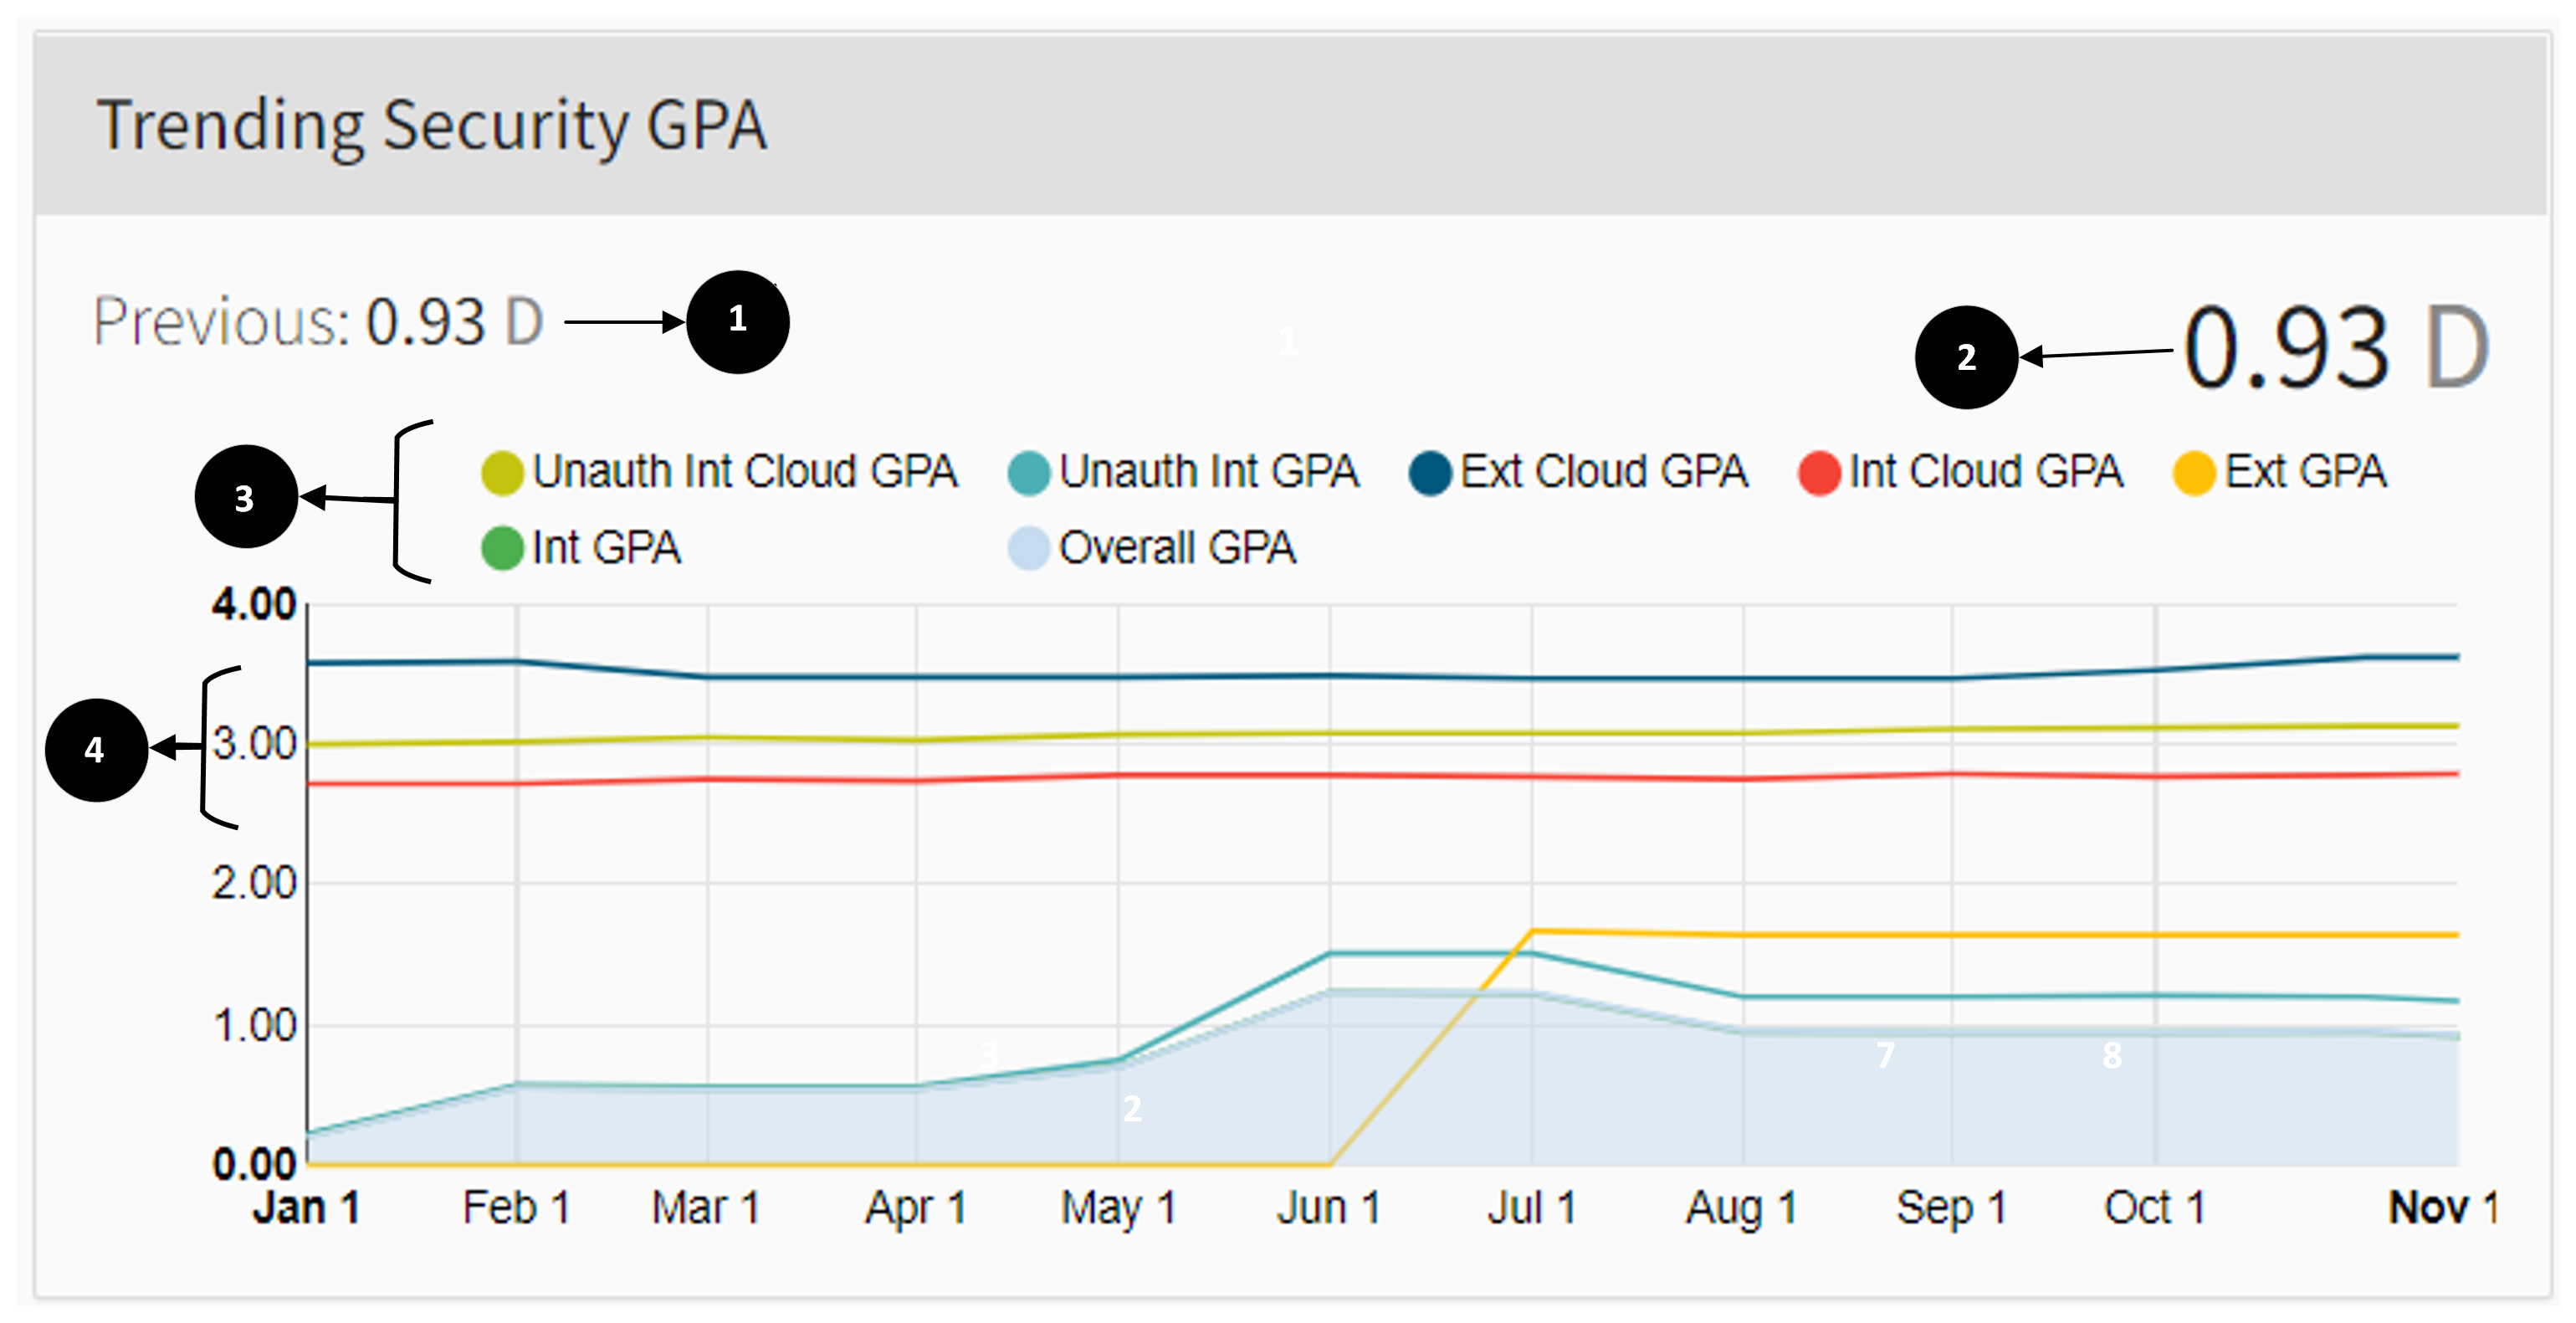
The Trending Security GPA panel shows changes to your Security GPA over time.
-
Your Security GPA before the most recent scan.
-
The Security GPA after the most recent scan.
-
Data sets shown as lines on the graph. Select a data-set label to show or hide it.
NOTE: Cloud GPA is an anonymous aggregate of customer data that you can use to compare your Security GPA with other organizations. -
The graph shows Security GPA trends over the past year and how changes in your environment affect the overall score.
TIP: Hover over a data point to view the Security GPA for that point in time.
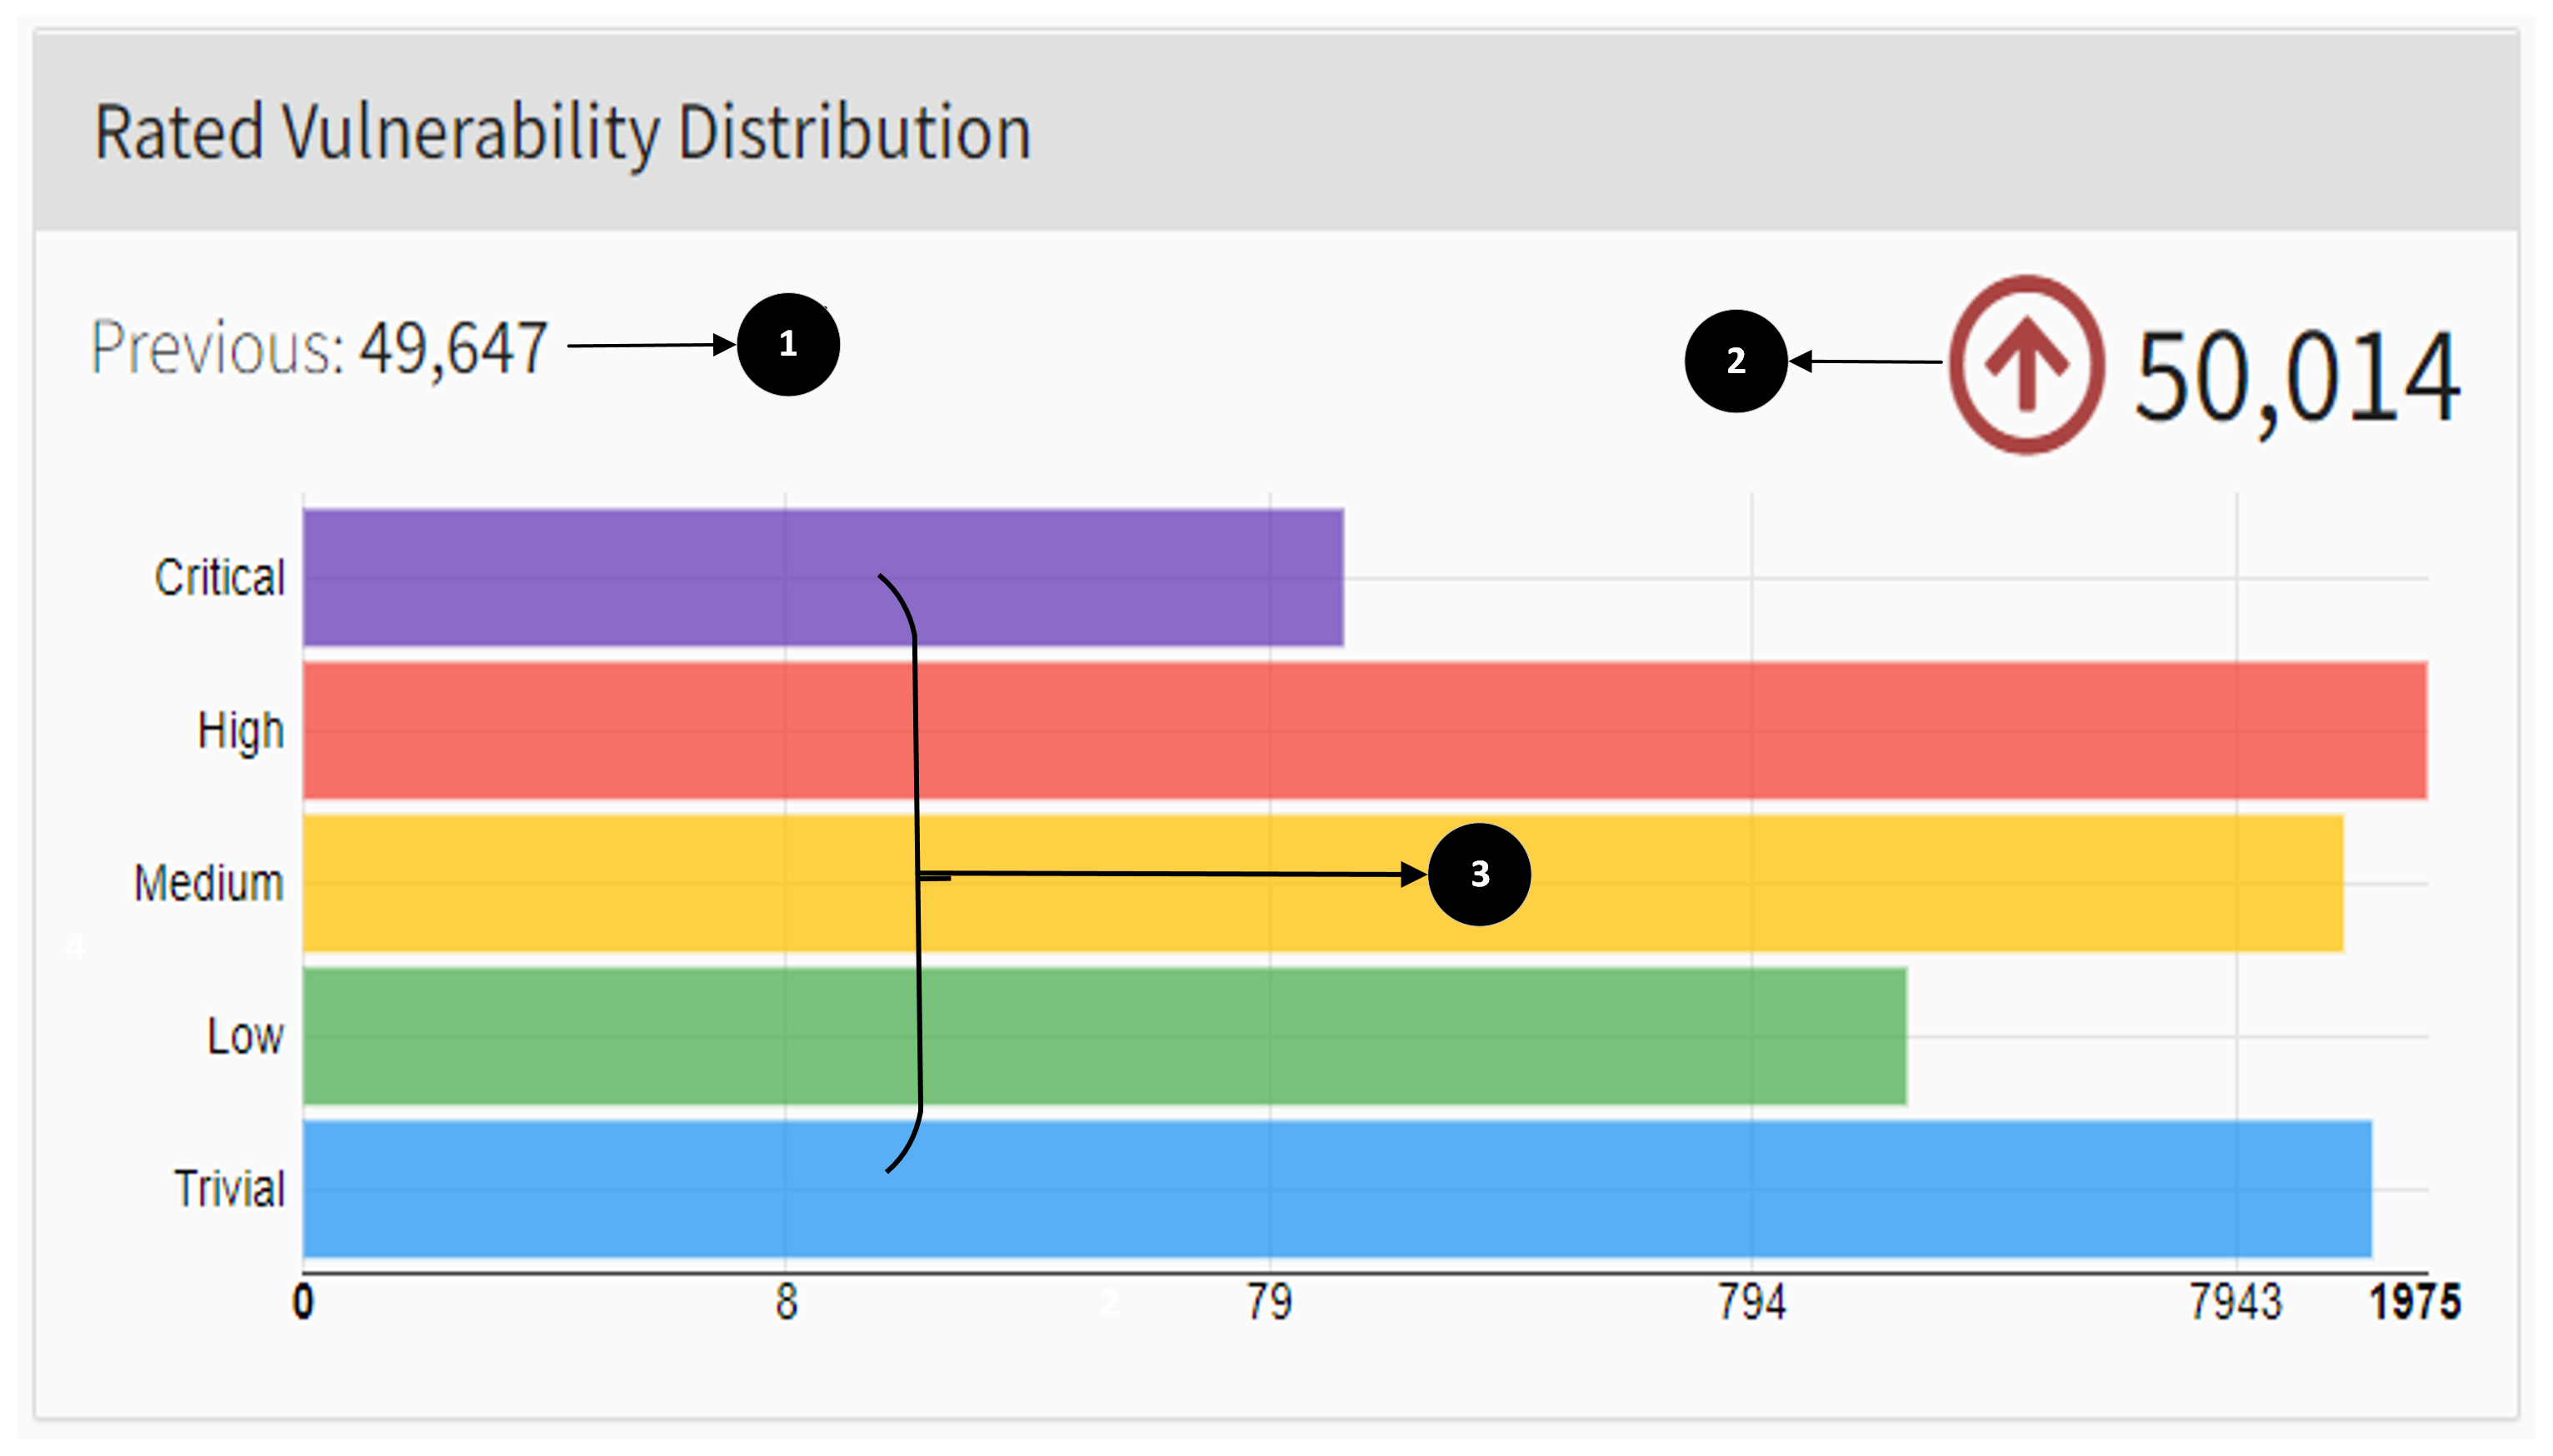
The Rated Vulnerability Distribution panel shows how vulnerabilities in your environment are distributed by severity.
-
The number of vulnerabilities detected before the most recent scan.
-
The number of vulnerabilities detected after the most recent scan.
-
Vulnerabilities grouped by severity:
-
Critical — Allows full system access and is easily exploitable.
-
High — Allows full system access but is not easily exploitable.
-
Medium — Allows some system access and partial control.
-
Low — Does not allow substantial system access but involved some information exposure.
-
Trivial — Tied to minor vulnerabilities but is not useful to an attacker.
TIP: Hover over or select a severity bar to view more information about vulnerabilities at that severity level. -
OWASP Top 10 Breakdown
WAS dashboard features this additional data panel. The (Open Web Application Security Project) OWASP Top 10 Breakdown panel shows the number of vulnerabilities in your environment that fall under each OWASP Top 10 risk. The OWASP Top 10 is a list of the most critical application security risks as determined by the OWASP and is a widely adopted AppSec benchmark.
Select an OWASP risk to see its related vulnerabilities.
See related: To learn more about the OWASP Top 10, see OWASP Top 10 Application Security Risks.
Assets At Risk
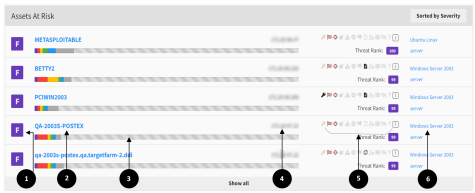
The Assets At Risk panel shows he five most vulnerable assets and lets you sort them by Severity or Threat Rank.
-
Asset's Security GPA.
-
Asset Name — Select to view vulnerabilities found on this asset.
-
Vulnerability severity distribution.
TIP: Hover over the severity graph to view details such as the number of medium-severity vulnerabilities detected on the asset. -
Asset IP address.
-
Asset status icons — Hover over an icon to view its description.
-
Asset operating system and type.
At-Risk Applications
For WAS, the At-Risk Applications panel shows the five most vulnerable web applications.
-
Web application Security GPA.
-
Web application name - Select the name to view vulnerabilities detected on the application.
-
Vulnerability severity distribution.
-
Web application status.
Vulnerabilities You Should Fix
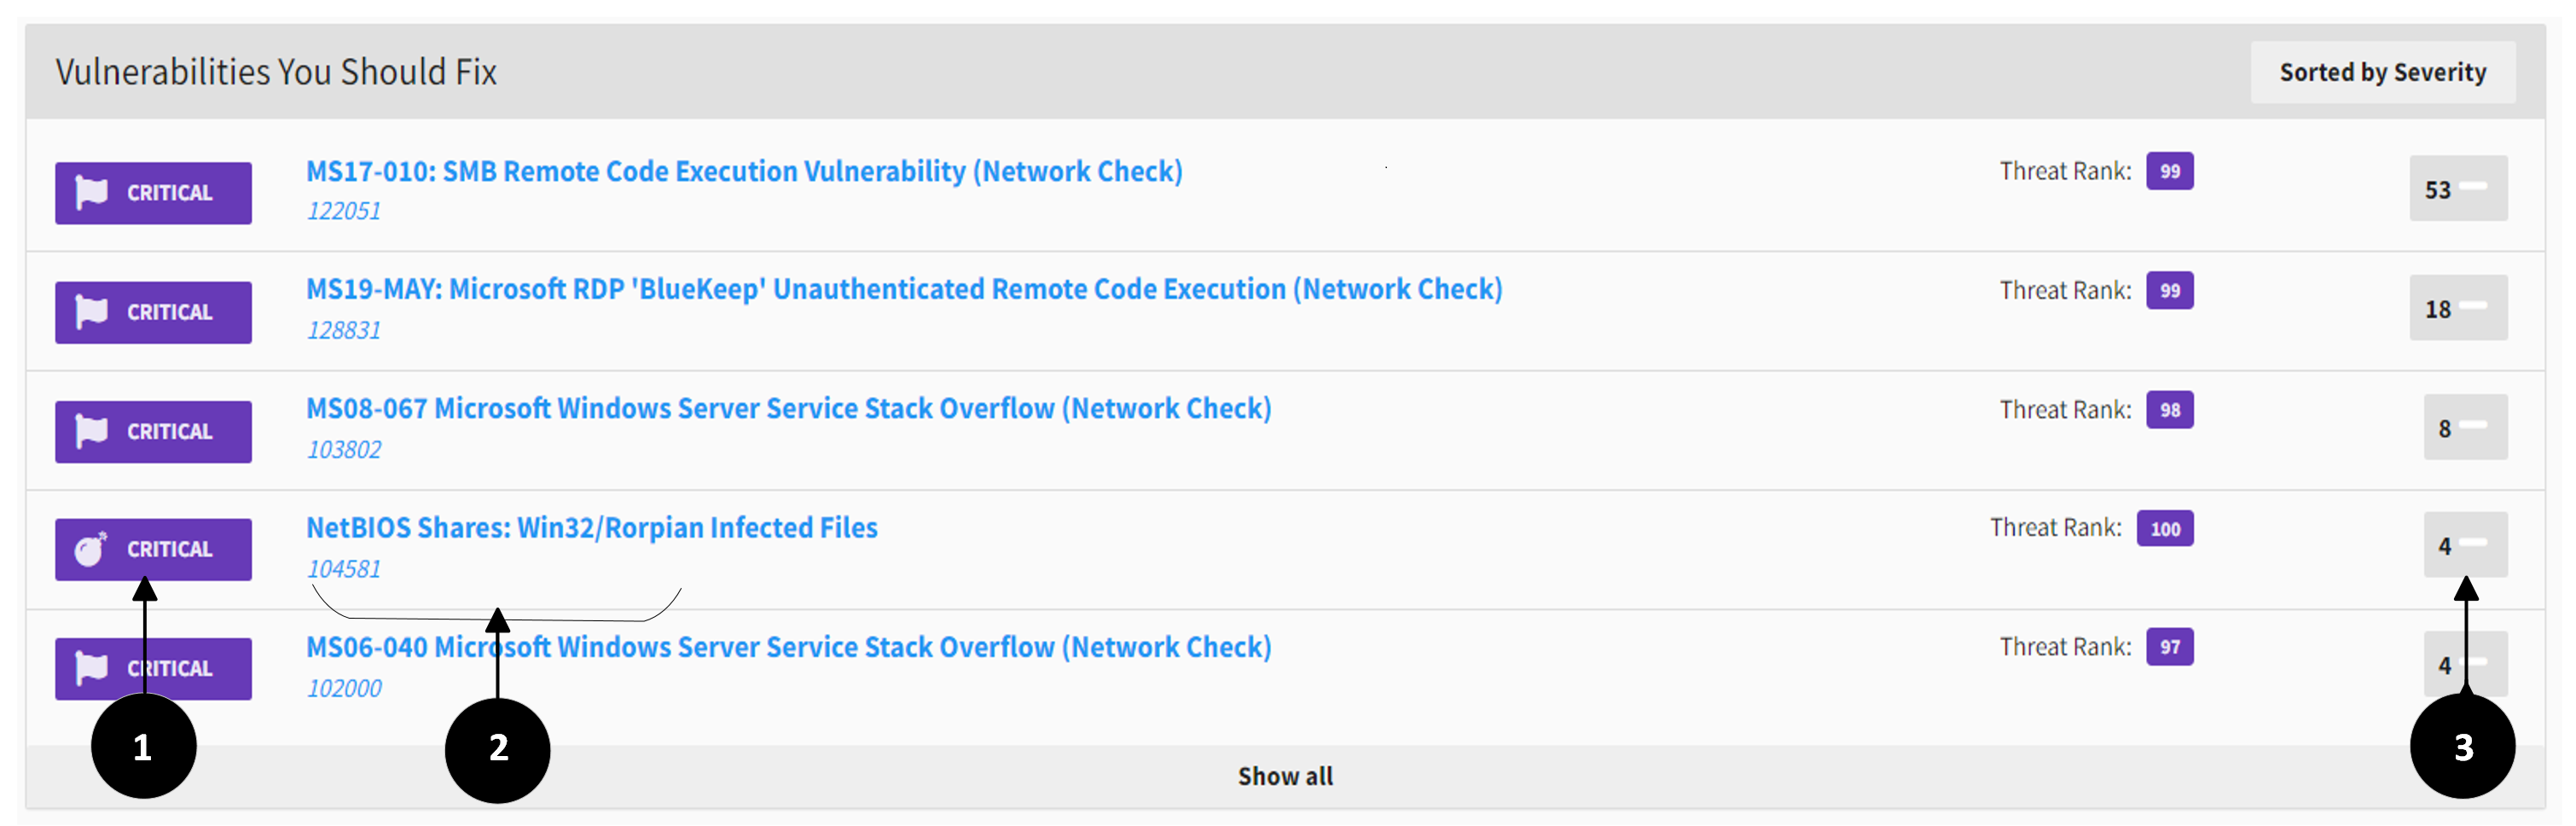
The Vulnerabilities You Should Fix panel shows the vulnerabilities that most need your attention. These can be sorted by Severity or Threat Rank.
-
Vulnerability class and severity level:
-
Explicit
-
Potential
-
Recon
-
Compliance
-
Malware
For more details, see What are vulnerability classes and severities?
-
-
Vulnerability description
-
Vulnerability instance on your environment
Recent Scanner Releases
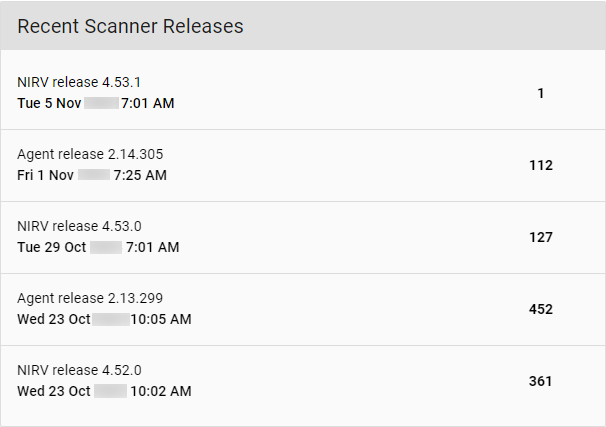
The Recent Scanner Releases panel provides information about Network Scanner
Recent Fortra VM Releases
The Recent Releases panel provides information about Fortra VM releases, including release notes.